0
Taps required from the user
A drop-in PAM module that adds Spriv's Adaptive MFA to SSH and sudo across your Linux and Unix estate no user interaction, no agent-side secrets to manage per host.
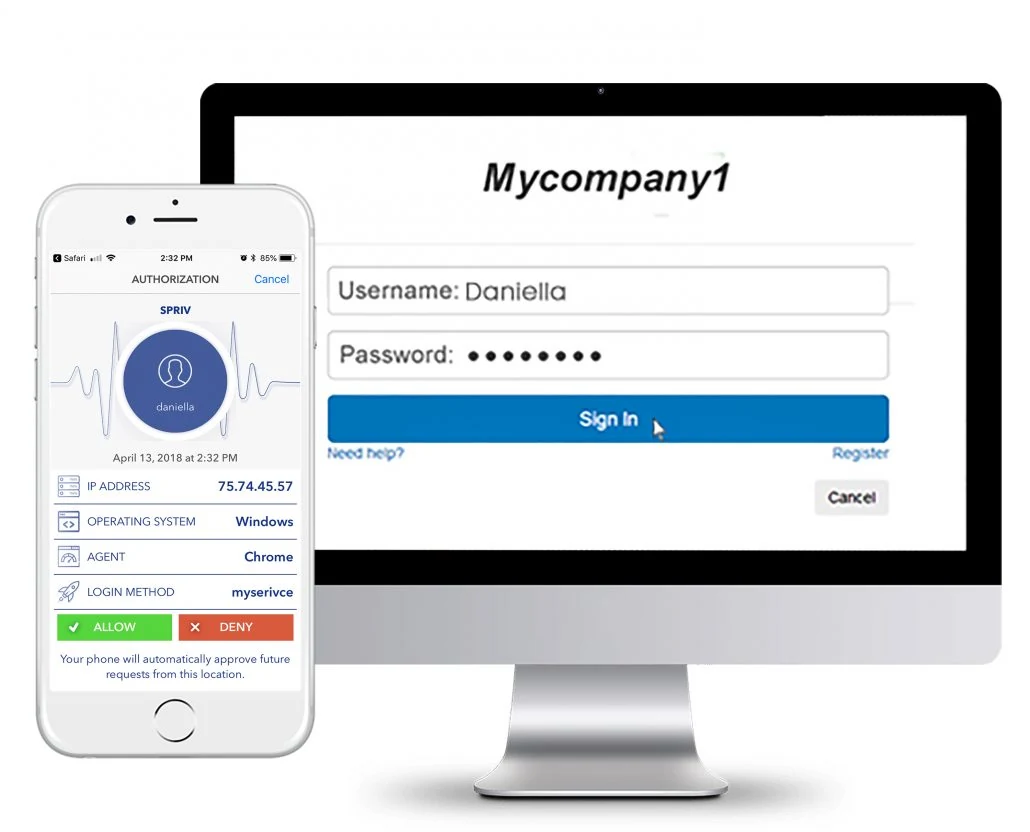
Spriv's PAM module hooks into the standard Linux and Unix authentication stack, so it protects SSH logins and sudo elevation the same way no separate agent for each surface, no changes to the applications your users already run.
Add the module to /etc/pam.d/sshd and /etc/pam.d/sudo, register the host in the Spriv admin console, and it's live. Configuration management tools (Ansible, Puppet, Chef) can push the same drop-in file across an entire server estate.
Once a user is paired, Spriv checks the workstation-phone pair silently during the PAM conversation. A match clears the login without a prompt; a mismatch falls through to a challenge, so nothing about the SSH or sudo flow itself has to change.
If the phone is unreachable or unpaired, Spriv falls back to SMS code, TOTP, or Allow/Deny so a network blip on the phone side never blocks an admin from reaching a server they're authorized on.
Two free users and two free servers on every plan. No credit card, install in under five minutes.